Experienced Leadership. Practical Security. Measurable Results.
Leneer Data Assurance Solutions is a cybersecurity governance, risk management, and compliance advisory firm helping cloud service providers, government contractors, and regulated organizations navigate complex federal cybersecurity requirements.
An Established Foundation. A Renewed Focus on Federal Cybersecurity.
Founded in 2008, Leneer Data Assurance Solutions has a history of supporting government and commercial organizations through cybersecurity, information technology, staffing, and management consulting services.
Built on Service, Technology & Trust.
Leneer established its foundation in professional services, cybersecurity, information assurance, technology support, and management consulting for government and commercial organizations.
Focused on the Future of Federal Security.
Building on our established capabilities, Leneer is strengthening its position as a specialized federal cybersecurity advisory firm supporting FedRAMP readiness, security governance, and sustainable compliance programs.
Compliance requires more than meeting individual requirements.
It demands coordinated leadership, technical understanding, defensible evidence, and processes that remain effective over time. We help organizations connect these elements into a coherent, sustainable cybersecurity program.
Cybersecurity & Information Assurance
Security governance, risk assessment, control evaluation, and practical cybersecurity oversight.
Federal Compliance & Risk Management
FedRAMP, FISMA, NIST frameworks, authorization readiness, and regulatory compliance advisory.
Program Management & Operational Support
Structured planning, stakeholder coordination, remediation management, and ongoing compliance operations.
Decades of Experience. Focused on Today's Federal Security Challenges.
Experienced cybersecurity leadership is essential to navigating complex regulatory requirements, managing risk, and building effective security programs.
Cybersecurity, risk management, privacy and regulatory compliance
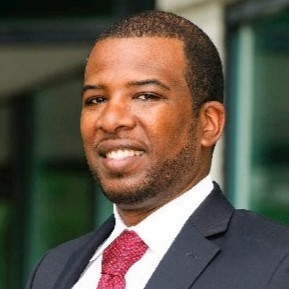
Robert E. Lester.
Leneer is led by Robert E. Lester, a cybersecurity governance, risk, privacy, and compliance professional with more than 20 years of experience supporting security and regulatory initiatives across complex organizational environments.
His professional background includes engagements involving federal agencies, government contractors, healthcare organizations, and other regulated industries where security governance, risk management, and compliance are essential to operations.
His experience encompasses federal security frameworks, authorization readiness, security assessments, compliance program development, IT auditing, privacy governance, and ongoing risk oversight.
Connecting regulatory requirements with practical security execution, informed decisions, and sustainable governance.
Recognized Expertise. Demonstrated Commitment.
FedRAMP & FISMA Compliance
Federal security requirements and authorization advisory
NIST Risk Management Framework
Risk-based governance and framework implementation
NIST SP 800-53 Assessments
Security control evaluation and assessment support
Federal Authorization Readiness
Security documentation and assessment preparation
Security Assessment & Remediation
Security gap analysis and corrective action management
Continuous Monitoring
Vulnerability governance and compliance oversight
Enterprise Risk & IT Auditing
Risk evaluation, internal controls and audit coordination
Privacy & Regulatory Compliance
Privacy governance, security policies and accountability
Federal Experience That Informs Practical Execution.
A documented history of supporting security, technology, governance, and compliance initiatives.
Leneer's background includes cybersecurity, information assurance, and technology engagements involving federal agencies and commercial organizations. Our historical portfolio reflects experience in authorization readiness, independent assessments, privacy governance, audit remediation, and security program support.
U.S. Department of Homeland Security
Leneer's historical capability portfolio identifies FedRAMP Authorization to Operate readiness support associated with the Department of Homeland Security's Customs and Border Protection environment.
Selected Engagements
U.S. Department of Labor
Authorization to Operate readiness, independent security assessments, and security program operational support.
U.S. Department of Health and Human Services
Independent security authorization assessment support within a federal healthcare environment.
Corporation for National and Community Service
Privacy program establishment and personally identifiable information inventory activities.
Pension Benefit Guaranty Corporation
Audit remediation and inventory assessment support, including activities related to a reported material weakness.
Experience Across Regulated Industries.
Our historical portfolio also includes commercial cybersecurity and compliance engagements supporting security governance, technical assurance, and risk management.
Crowley Shipping
ISO 27001 implementation support
Trusted Health Plan
Healthcare data analytics and vulnerability and penetration testing
Merck Pharmaceuticals
Security policy and procedure gap analysis
General Dynamics
Intrusion detection, analysis, remediation, and contingency planning
Our experience across federal and regulated environments informs a practical approach to security governance, compliance readiness, and long-term risk management.
EXPERIENCE THAT SUPPORTS EXECUTIONRepresentative engagements are drawn from Leneer's historical company capability statement. References describe past performance and do not imply current contracts, agency endorsements, or authorization to represent the organizations listed.
Built for the Next Era of Federal Cloud Security.
Federal cybersecurity requirements continue to evolve, placing greater emphasis on demonstrable security outcomes, reliable evidence, and continuous accountability.
Leneer helps organizations understand applicable requirements, assess their readiness, and establish practical security and compliance capabilities.
FedRAMP 20x
Helping cloud service providers prepare for evolving federal security expectations through structured readiness, governance, evidence strategies, and continuous assurance.
FedRAMP 20x Readiness Assessment
Evaluate current security capabilities, identify compliance gaps, and establish prioritized implementation roadmaps.
Certification Program Management
Coordinate compliance planning, documentation, evidence preparation, remediation, and assessment readiness.
Key Security Indicator Implementation
Translate applicable security indicators into measurable practices, technical validation, and defensible evidence.
Security Decision Record Development
Support documented security decisions, implementation rationale, verification activities, and supporting evidence.
Managed Continuous Monitoring
Support vulnerability oversight, remediation tracking, compliance reporting, and ongoing security governance.
FedRAMP Rev. 5 Transition Support
Help organizations maintain existing compliance obligations while evaluating applicable program changes.
Virtual FedRAMP Program Management
Experienced advisory leadership for compliance governance, stakeholder coordination, milestone management, and executive reporting.
Building compliance capabilities that last.
Our objective is not simply to help organizations prepare for an assessment. It is to help them establish security governance, operational processes, and evidence practices that remain effective over time.
Are You Ready for FedRAMP 20x?
The transition to FedRAMP 20x is underway. Understanding your organization's readiness today can help prevent costly remediation delays tomorrow.
Schedule a FedRAMP Readiness Consultation
Speak with an experienced federal cybersecurity advisor about your certification goals, compliance challenges, and next steps.
Leneer Data Assurance Solutions is an independent cybersecurity advisory firm and is not affiliated with, endorsed by, or authorized to issue certifications on behalf of the FedRAMP Program.
Driven by Purpose. Defined by Impact.
Our mission and vision reflect a commitment to helping organizations move beyond fragmented compliance activities toward effective security governance, meaningful risk management, and lasting confidence.
Simplify Federal Compliance. Strengthen Security. Build Lasting Confidence.
Our mission is to help cloud service providers, government contractors, and regulated organizations simplify federal cybersecurity compliance, strengthen their security posture, and establish sustainable programs that support ongoing readiness.
Through experienced leadership, practical advisory support, and risk-informed guidance, we help organizations turn complex requirements into clear priorities, accountable actions, and measurable progress.
A Future Where Compliance Demonstrates Real Security.
We envision a federal cloud ecosystem where cybersecurity compliance is not treated as a periodic documentation exercise, but as an integrated part of everyday security operations.
In this future, organizations use continuous evidence, effective governance, and clear accountability to demonstrate security capabilities, manage emerging risks, and maintain confidence among federal stakeholders.
Practical security. Sustainable compliance. Federal cloud confidence.
Compliance Should Demonstrate Security. Not Just Document It.
Effective cybersecurity is not measured by the volume of documentation produced. It is demonstrated through sound decisions, functioning security controls, credible evidence, and consistent accountability.
At Leneer, five core principles guide our approach to federal compliance advisory, security governance, and long-term risk management.
Security outcomes should drive compliance decisions — not the other way around.
01 Security Before Paperwork
Documentation should reflect real, functioning security practices. We prioritize effective controls, meaningful risk reduction, and operational security before producing compliance artifacts.
02 Risk-Informed Decisions
Security priorities should be informed by actual threats, vulnerabilities, business context, and regulatory obligations. We help organizations direct resources toward the risks that matter most.
03 Evidence-Based Assurance
Security claims should be supported by credible, verifiable evidence. We emphasize measurable indicators, documented decisions, and assessment-ready records that demonstrate security effectiveness.
04 Practical & Sustainable Implementation
Compliance programs must work within real operational constraints. We recommend achievable processes, clear responsibilities, and scalable security practices that organizations can sustain.
05 Continuous Accountability
Security governance does not end after an assessment or authorization milestone. We emphasize continuous monitoring, clear ownership, management visibility, and timely remediation.
Five principles. One consistent commitment to meaningful security outcomes.
Practical guidance. Defensible decisions. Sustainable security.
Experience You Can Trust. Guidance You Can Act On.
Choosing a cybersecurity advisory partner requires more than technical knowledge. It requires experience, clear communication, disciplined execution, and an understanding of the operational realities behind federal security requirements.
Established Experience. Focused Expertise. Practical Results.
We combine an established company foundation with experienced cybersecurity leadership and specialized advisory capabilities to help organizations address complex compliance challenges with clarity and confidence.
Established Business Foundation
Founded in 2008, Leneer brings an established organizational history spanning cybersecurity, information assurance, staffing, and management consulting services.
20+ Years of Leadership Experience
Leadership experience across cybersecurity governance, risk management, privacy, federal compliance, security assessments, and IT auditing.
Federal Security Framework Expertise
Knowledge of FedRAMP, FISMA, NIST Risk Management Framework, NIST SP 800-53, and related federal cybersecurity requirements.
Specialized FedRAMP Advisory
A focused advisory offering covering FedRAMP 20x readiness, security indicators, evidence strategies, continuous monitoring, and program management.
Practical, Business-Aligned Recommendations
Guidance designed around actual security risks, business objectives, technical capabilities, and organizational constraints.
Flexible Engagement Models
Advisory support tailored to organizational needs, from focused readiness assessments and project engagements to ongoing program management and compliance oversight.
Leadership-Level Visibility
Clear communication, documented priorities, milestone tracking, and executive reporting to support informed security and compliance decisions.
We bring structure to complexity, clarity to security decisions, and practical direction to federal compliance challenges.
A Clear Path From Complexity to Confidence.
Federal cybersecurity programs demand disciplined planning, technical understanding, and ongoing accountability. Our five-stage advisory approach helps organizations establish priorities, coordinate execution, and maintain meaningful security outcomes.
Understand Before Acting.
Every effective cybersecurity program begins with a clear understanding of the organization. We work to understand business objectives, technology environments, federal compliance obligations, stakeholders, and existing security governance.
- Stakeholder discussions
- Business and security objectives
- System and environment review
- Regulatory applicability
- Existing program documentation
Defined engagement scope and initial program understanding
Identify Gaps. Understand Risk.
We evaluate current security practices against applicable requirements and organizational objectives. This includes identifying control gaps, operational weaknesses, evidence deficiencies, and risks that may affect readiness.
- Security control review
- Compliance gap identification
- Evidence readiness evaluation
- Risk and vulnerability review
- Findings documentation
Readiness assessment and prioritized gap register
Turn Findings Into Direction.
Assessment findings become an actionable roadmap. We help establish priorities, define responsibilities, identify dependencies, and develop realistic implementation milestones aligned with security needs and business capacity.
- Risk-based prioritization
- Remediation planning
- Milestone development
- Responsibility assignment
- Stakeholder alignment
Security and compliance implementation roadmap
Translate Plans Into Progress.
We provide advisory and program management support as organizations implement security improvements, address findings, prepare compliance evidence, and coordinate readiness activities across responsible teams.
- Remediation coordination
- Security governance support
- Evidence development
- Progress and milestone tracking
- Assessment preparation
Documented implementation progress and readiness evidence
Maintain Confidence. Strengthen Over Time.
Security and compliance require ongoing attention. We help organizations establish monitoring, reporting, accountability, and improvement practices that support sustainable operations beyond initial readiness or assessment milestones.
- Continuous monitoring oversight
- Remediation status tracking
- Management reporting
- Evidence maintenance
- Continuous improvement planning
Sustainable monitoring and governance operating practices
A Process Built Around Real-World Execution.
Our approach is adaptable to each organization's maturity, environment, and regulatory obligations. Engagements may cover a single stage or extend across the full advisory lifecycle.
Build Federal Cloud Confidence With Experienced Leadership.
Whether your organization is preparing for FedRAMP 20x, addressing federal compliance gaps, or strengthening continuous security monitoring, Leneer can help you define a practical path forward.
Connect with our leadership to discuss your priorities, understand your current challenges, and explore advisory support aligned with your organization's needs.
FedRAMP Readiness. Continuous Assurance. Federal Cloud Confidence.